Highlight
Successful together – our valantic Team.
Meet the people who bring passion and accountability to driving success at valantic.
Get to know usManaged extended detection & response
valantic MXDR gives you round-the-clock, investigation and response across your entire attack surface, built natively on Microsoft Sentinel and Defender, accelerated by AI and delivered by a Europe-based SOC.
74%
of breaches involve the human element
21 days
average dwell time before detection
€4.5M
the average cost of a data breach in Europe is €4.5M
NIS2
compliance is now mandatory across an expanding range of sectors
Organisations need a trusted security partner — not just tools.
Technology alone doesn’t make a security operation trustworthy — the people and the process behind it do. valantic MXDR is delivered by a dedicated European team who treat your environment as their own: a named Service Delivery Manager who knows your business, analysts who tune detections to your actual risk profile rather than shipping generic rulesets, and a governance rhythm that keeps your leadership informed in language it can act on.
We see this as a partnership, not a subscription.
24/7 SOC monitoring
Continuous detection and response, including nights, weekends and holidays.
A named local contact
A dedicated Service Delivery Manager, not a rotating ticket queue.
EU-based SOC, GDPR-native
Data processed and stored exclusively within the EU.
Deep Microsoft specialisation
we deploy, tune and operate Sentinel and Defender, not just resell licences.
Prevention-minded, detection-led
We reduce attack surface proactively, not just detect after the fact.
Business-aligned reporting
quarterly governance and executive reporting in the boardroom’s language.
endpoint, network, identity & behaviour
All telemetry — including Network Telemetry and UEBA — unified and correlated in a single platform.
| Endpoints (EDR) | PCs, servers, workstations, via Defender for Endpoint |
| Network Telemetry | lateral movement and C2 detection |
| Identity | sign-ins and privilege changes, via Defender for Identity |
| Cloud & SaaS | Azure, M365, Teams, SharePoint |
| UEBA | user & entity behaviour analytics, insider threat and anomaly detection |
| Threat Intelligence | global IOC & threat feeds, real-time enrichment |
| Business-critical applications | ERP, finance & line-of-business systems, onboarded via available logs |
SOAR playbooks and AI handle triage, enrichment and containment automatically; analysts focus on what truly needs human judgment.
We proactively reduce attack surface and stop incidents before they escalate.
Azure Logic Apps evaluate and tag every alert by severity the moment it arrives.
A single pane of glass with real-time dashboards, live incident status, SLA tracking and full reporting.
Incidents flow directly into existing ITSM workflows, no parallel systems, no manual re-keying.
Standardised, version-controlled, auditable and repeatable onboarding governance.
Technology detects; people decide; process makes the response repeatable. valantic MXDR runs on three reinforcing layers:
MXDR — powered by microsoft defender
If your organisation already invests in Microsoft 365 or Azure, MXDR maximises the value of your existing licensing rather than adding another vendor stack.
Microsoft Sentinel
SIEM + SOAR, the SOC brain, correlating telemetry at scale.
Defender for Endpoint
EDR for workstations and servers.
Defender for Identity
Identity threat detection and response.
Defender for Cloud
Cloud workload protection across Azure and multi-cloud.
Defender for Office 365
Email, Teams and SharePoint protection.
Defender for Cloud Apps
SaaS and shadow IT visibility.
valantic gets more out of Microsoft Sentinel and Defender than you would alone.
We manage the full stack — proactive tuning, optimisation, and continuous enrichment with the latest threat intelligence — so your investment in the Microsoft Security Suite actually pays off: stronger resilience, faster response, and SIEM and XDR working as one system, not two.
And because it's native Microsoft, you're never behind.
We continuously evaluate new Microsoft security capabilities as part of the service and activate relevant functionality together with the customer, depending on technical and licensing requirements.
Your way to a production-ready soc
For customers with an existing Microsoft Sentinel environment, onboarding and transition to threat detection can typically be achieved within 4–6 weeks. Greenfield implementations are scoped individually depending on the existing infrastructure and requirements.
Every transformation changes not only how a company works but also where it is exposed. Standalone MXDR providers usually only step in once the new landscape is live, whereas valantic is part of the journey from the very beginning. It helps clients transform their business and IT landscape, secures that transformation along the way and continues to operate the security layer once the project is complete. As a result, MXDR is no isolated service but an integral part of valantic’s broader Security & Transformation proposition.
This way, clients work with one partner who is responsible for both transformation and security, from the first workshop through to daily operations.
Obliges EU member states to impose stricter cybersecurity regulations and enforce them more consistently.
LEARN MORE LEARN MORE
Blog · March 17, 2025
In 2025, banks and their service providers will face a multitude of new challenges: Cyberattacks are on the rise, digital dependencies are growing and DORA is bringing profound changes. But which aspects will the supervisory authorities be monitoring most critically in 2025?
Learn more National Supervisory Programme 2025-2027: Focus on Cyber Resilience and DORA
an experienced team, reliable partners and seamless preparation to act immediately when a cyber crisis happens.
LEARN MORE LEARN MORE

Cyber crises happen. The decisive factor is what happens next. Our Incident Response Service enables you to act immediately.
LEARN MORE LEARN MORE
Together, we develop a customized package of preventive measures and complement it with an “early warning system” – our darknet monitoring.
LEARN MORE LEARN MORE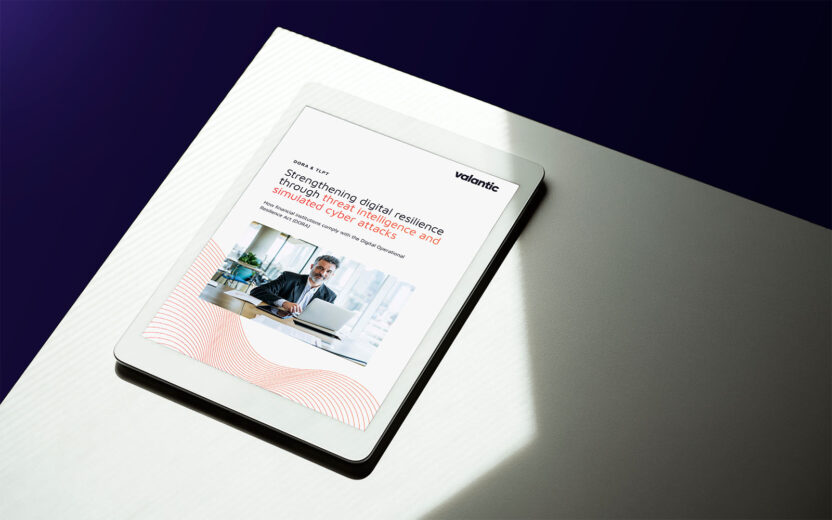
Download
This white paper explores, how banks and financial service providers can meet the EU’s Digital Operational Resilience Act (DORA) requirements through threat intelligence and TLPT-based cybersecurity strategies to ensure long-term operational resilience.
Download White paper: DORA & TLPT – Strengthening digital resilience through threat intelligence and simulated cyber attacksYour valantic experts
Thomas Lang
Partner & Managing Director
valantic Division Digital Strategy & Analytics
Hermann Friesen
Vice President of Cybersecurity Sales
valantic